Autonomous DAST + SAST + AI remediation

AI wrote your code in minutes. Find every exploit before hackers do.

A 200+ check security audit across OWASP ZAP, Nuclei, Semgrep and Playwright in 3 minutes — with 1-click fix prompts for Cursor and Claude Code.

Non-destructive security scan completes in 3 to 5 minutes
  • Non-destructive
  • Safe Harbor compliant
  • DNS TXT verified
Security shield protecting web applications from bugs

Securing apps built with your favourite AI tools

CursorCopilotBoltv0WindsurfClaude CodeNext.jsSupabaseFastAPIFirebaseVercelReplitCursorCopilotBoltv0WindsurfClaude CodeNext.jsSupabaseFastAPIFirebaseVercelReplit
What we offer

Two ways to secure what you ship

Scan any site in minutes, or keep every release covered with a continuous security program.

Automated

Website & URL Scanner

Enter a URL and get a multi-engine audit in 3 minutes — leaked keys, open APIs, missing headers and framework CVEs, scored 0–100.

  • 200+ OWASP & CVE checks
  • Unblurred fix prompts
  • Unlimited single-finding retests
Scan a website
Website & URL Scanner
Continuous

Always-on Pentest Program

Recurring audits for every release, mapped to OWASP Top 10, CWE, SOC 2, ISO 27001 and DPDP Act 2023, with board-ready PDF reports.

  • 15+ page executive PDF
  • Compliance control mapping
  • Embeddable live trust seal
See sample report
Always-on Pentest Program
Your control center

One dashboard for your entire attack surface

Every scan, finding, fix and retest — organised so founders, developers and auditors see exactly what matters.

Open the live dashboard
app.hackmywebsite.io/dashboard
app.acmefintech.ioContinuous Monitoring
Updated 14 mins ago
AI Launch Score
92/ 100
+14 pts vs last audit
Vulnerability Status
0Crit2High
3 patches auto-verified
Perimeter Coverage
200+
DAST, CVE & Secrets
4-Week Launch Readiness TrajectoryTarget Threshold: 85/100
68
Sep 24
76
Oct 02
85
Oct 10
92
Oct 18
Global coverage

Built in India. Protecting apps worldwide.

Scans run from distributed infrastructure, checking your perimeter the way real attackers see it — from anywhere.

200+
Security checks
4
Scan engines
3 min
Average audit
24/7
Engine uptime
Multi-engine coverage

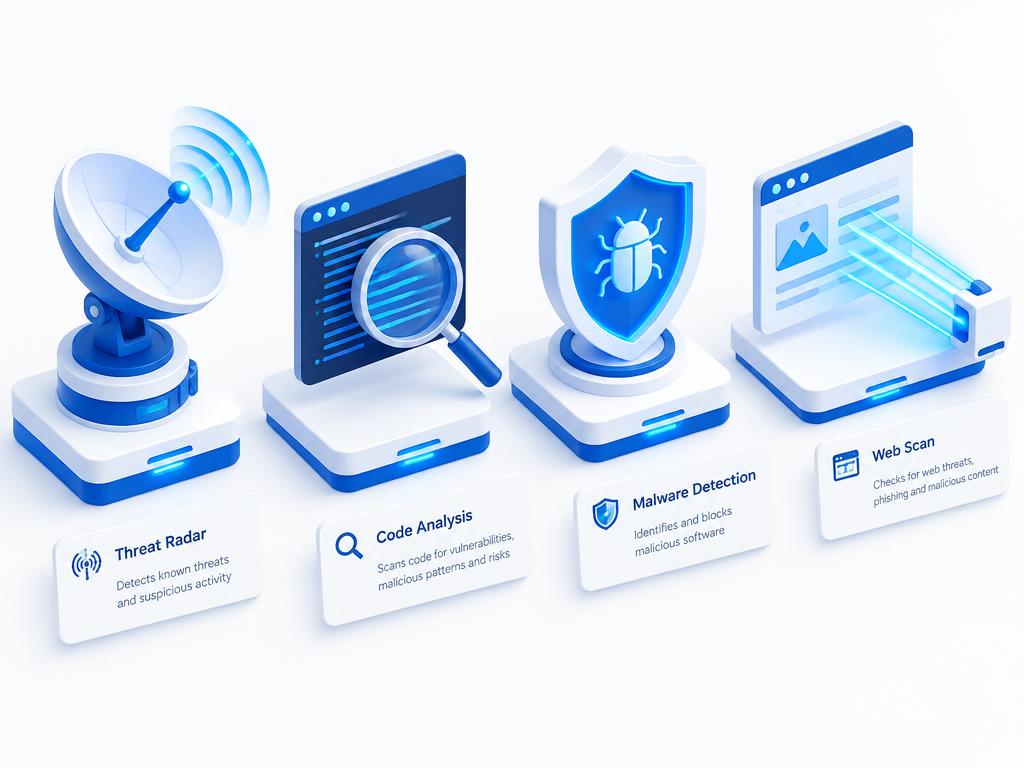
Four engines. 200+ checks. One deterministic score.

Runtime crawling, CVE templates, static analysis and headless rendering run in parallel — then findings are de-duplicated and mapped to compliance controls.

200+
Security checks
3 min
Average scan
0
Downtime caused
OWASP ZAP Engine logoActive Daemon
RUNTIME DAST

OWASP ZAP Engine

Crawls public and authenticated routes to uncover reflected/stored XSS, SQL injection, CSRF, broken auth headers, and insecure cookies without downtime.

200+ Curated Nuclei Rules logoNuclei v3.3
CVE TEMPLATES

200+ Curated Nuclei Rules

Detects exposed .env and .git directories, open Swagger/GraphQL introspection, cloud bucket misconfigurations, and known framework CVEs.

Semgrep SAST & Secret Audit logoGitHub App #4518222
STATIC AST

Semgrep SAST & Secret Audit

Scans source repositories and client JS bundles for hardcoded API keys, Stripe/Supabase service tokens, and insecure JWT validation logic.

Playwright SPA Surface Discovery logoPlaywright Engine
HEADLESS DOM

Playwright SPA Surface Discovery

Renders modern React, Next.js, Vue, and Nuxt single-page applications to inspect client-side routes, shadow API calls, and PostMessage wildcards.

Perimeter Posture
THREAT INTEL

Safe Browsing, SSL & DNSSEC

Audits Google Safe Browsing v4 reputation, TLS 1.3 cipher strength, SPF/DKIM/DMARC email spoofing defenses, and IP blacklist status.

SOC 2 / ISO / DPDP
TRUST & COMPLIANCE

Executive PDF & Live Trust Seal

Exports 15+ page board-ready PDF reports mapped to OWASP Top 10, CWE, SOC 2, ISO 27001, and DPDP Act 2023 controls plus an embeddable badge.

How it works

Verified, scanned and gated in three steps.

  1. 01
    Verify Domain via DNS TXT or HTML File
    MANDATORY LEGAL GATE~15 SECONDS

    Verify Domain via DNS TXT or HTML File

    Prevents unauthorized third-party scanning and guarantees 100% Safe Harbor compliance across production environments.

  2. 02
    DAST + Nuclei CVEs + Semgrep SAST + Threat Intel
    4-ENGINE PARALLEL AUDIT3–5 MINUTES

    DAST + Nuclei CVEs + Semgrep SAST + Threat Intel

    Combines runtime crawling with Google Safe Browsing v4, SSL/TLS cipher grading, and SPF/DKIM/DMARC/DNSSEC posture checks.

  3. 03
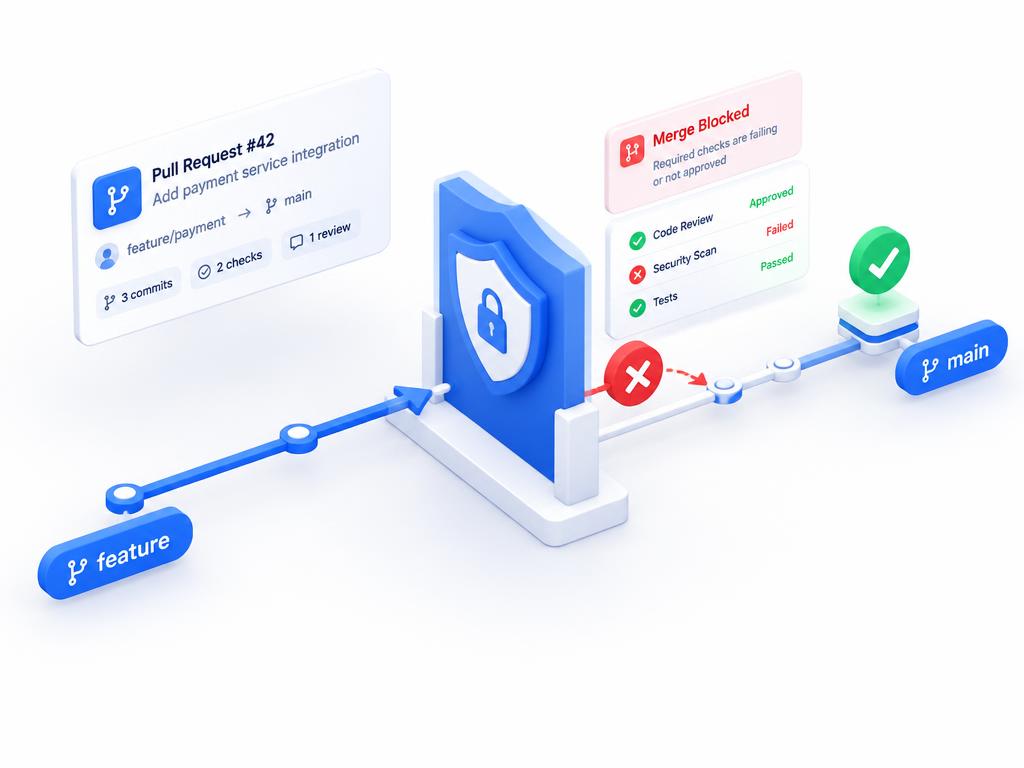
    Block Vulnerable Pull Requests Before Production
    GITHUB MERGE GATE (#4518222)CI/CD AUTOMATED

    Block Vulnerable Pull Requests Before Production

    Install the official GitHub App (#4518222) to enforce a minimum AI Launch Score threshold (e.g. 85/100) on every PR merge.

Stack-aware testing

Checks written for the way AI tools actually build apps.

Generic scanners miss framework-specific mistakes. Pick your stack to see what we test first.

NEXT.JS SERVER ACTIONSCRITICAL CHECK

Unauthenticated Server Actions & /api Routes

AI coding tools frequently generate Next.js 15 Server Actions and Route Handlers that mutate database state without verifying session tokens inside the handler.

CLIENT BUNDLE LEAKSHIGH CHECK

NEXT_PUBLIC_ Secret Prefix Misconfigurations

Semgrep SAST + Playwright inspect compiled Webpack/Turbopack chunks to catch private OpenAI, Stripe, and Firebase Admin keys accidentally bundled into client JS.

SECURITY HEADERSMEDIUM CHECK

Missing CSP, HSTS & SourceMap Exposure

Audits production next.config.js headers and checks whether .js.map files are leaking your entire proprietary TypeScript source tree to the public.

For agencies, freelancers & VAPT consultants

Turn 5-minute audits into a recurring security retainer.

The Agency plan (₹4,999/mo) covers 10 client domains, unlimited automated scans, and 100% white-label PDF reports with your logo, executive summary and compliance mapping.

  • Your logo and domain on every report
  • SOC 2, ISO 27001 & DPDP control tags
  • Dedicated WhatsApp & Slack support
Security engineers reviewing a client vulnerability report
Retainer calculator

Estimate monthly revenue from reselling audits.

Client websites6
110 included
Billing at ₹15,000 / audit
₹90,000
Agency plan
− ₹4,999
Estimated monthly margin
₹85,001
Preview white-label report
Transparent Subscription Tiers

Predictable Pricing for Founders & Agencies

Choose a plan to run unblurred scans, get AI remediation prompts, and unlock white-label client security deliverables.

Domestic UPI & Card billing enabled

Free

Instant security scanning to identify vulnerability risks with blurred dashboard findings.

₹0per month
  • 1 website target
  • 1 scan per month
  • 3 complimentary targeted retests
  • Executive PDF summary report
  • Blurred vulnerability details preview
  • DNS & HTML domain verification

Starter

For solo founders who want full unblurred security reports and instant code fixes.

₹1,999per month
  • 1 website target
  • 3 unblurred full scans per month
  • Unlimited targeted finding retests
  • Full unblurred 15+ page PDF security report
  • 6-dimension AI Launch Score evaluation
  • 1-click Cursor & Claude Code fix prompts
  • Standard email support
Most Practical

Pro

The most practical tier for growing startups with GitHub integration and API fuzzing.

₹2,999per month
  • 3 website targets
  • 10 unblurred full scans per month
  • Unlimited targeted finding retests
  • Full unblurred PDF & executive reports
  • AI Launch Score & 1-click IDE fix prompts
  • GitHub repo integration (automated SAST scan)
  • API & GraphQL endpoint fuzzing
  • Priority scan queue (fast 3-minute turnaround)

Agency

Built to be resold. Run continuous security audits across 10 client targets, export white-label reports, and bill ₹15,000+ per audit.

₹4,999per month
  • Everything in Pro included
  • 10 client website targets
  • Unlimited automated security audits
  • White-label PDF reports with your custom agency branding
  • OWASP Top 10 & CWE vulnerability categorization
  • Compliance reference tagging (SOC 2, ISO 27001, DPDP controls)
  • Multi-client target dashboard & shareable audit links
  • Dedicated agency WhatsApp & Slack support channel
Enterprise & InstitutionsDedicated Continuous Security Retainer

Custom Continuous Security Infrastructure for Engineering Teams

Dedicated security automation for organizations requiring custom Semgrep SAST rule authoring, auditor-ready vulnerability reports for SOC 2 & ISO 27001 evidence, dedicated static egress IPs for WAF bypass, and 100% in-house sovereign data isolation under strict Enterprise NDA.

Auditor-Ready Executive Assessment Reports
Dedicated Static Egress IP for WAF Whitelisting
Custom Semgrep SAST Rule Authoring
Automated GitHub & GitLab PR Merge Blocker Bot
Vendor Security Questionnaire Support (CAIQ / VSAQ)
Strict Enterprise NDA, Zero 3rd-Party Sharing & PO Billing
Starting At
₹1,49,000 / year
Custom scope • Net-30 payment terms
Schedule Enterprise Consultation
Frequently Asked Questions

Clear Answers for Engineering Teams

Everything you need to know about our scanning methodology, domain authorization, and remediation workflows.

Hack My Website scans your target website or API across 200+ automated vulnerability checks combining runtime DAST (OWASP ZAP), CVE exploit templates (Nuclei), static code analysis (Semgrep), and custom SaaS misconfiguration engines.